A Brand-New Outlook on Alternative Legal Service Providers in 2025
Traditionally, alternative legal service providers (ALSPs) are seen as providers of cost-effective solutions for high-volume, low-complexity tasks like contract management and document review. Over the past several years, ALSPs have transformed into strategic partners for law firms and corporate legal departments. They now provide specialised expertise and prioritise leveraging technology to enhance efficiency, foster innovation, and deliver value in legal operations. The start of 2025 represents not just a fresh start but an opportunity to further shift perspectives and reimagine how legal services could be delivered. Why 2025 Is a Turning Point Why should 2025 be any different from previous years? While budget and resourcing constraints are nothing new, the pressure to leverage technology—particularly genAI—to operate more efficiently and cost effectively has never been greater. For legal department leaders, the demand for smarter workflows, better metrics and flexible, scalable resourcing is impossible to ignore. Demonstrating cost-effectiveness and innovation continues to challenge law firms, with clients expecting more value than ever before. For many firms, ALSPs have emerged as valuable partners providing their expertise, scalable resources, and creative solutions. Similarly, corporate legal departments are grappling with mounting workloads driven by increasingly complex regulatory frameworks, rising litigation, and internal investigations. Without careful oversight, external counsel fees can escalate rapidly, adding further pressure to already stretched budgets. A strong partnership with an ALSP offers legal teams a wealth of advantages, including access to specialised talent. The ability to provide this expertise eliminates the time and effort of recruiting and training new employees who have the requisite skillsets. Teams instead can simply tap into those available within an ALSP. Read Here ALSPs also provide flexible resourcing options, and innovative technology solutions to support legal services delivery. These partnerships enable legal teams to manage fluctuating workloads seamlessly, tapping into expertise that may not be readily available in-house. ALSPs also bring advanced processes that streamline routine tasks like document review, significantly enhancing operational efficiency. By leveraging these resources, lawyers can focus on high-value strategic work, improve service delivery, and meet the growing expectations of their clients and internal stakeholders. Last but certainly not least, working with an ALSP and a team of experts, with knowledge of a specific technology and advanced workflows, can help reduce implementation obstacles and help teams to both increase the speed of adoption on the return on investment of a new tech solution. Are ALSPs an “Alternative” Option for Legal Services Today? Historically, ALSPs faced some scepticism from the legal industry, often rooted in misconceptions about their capabilities or quality of work. We have often used the term “perceived risk”, reflecting concerns about outsourcing sensitive legal tasks or entrusting non-traditional providers with tasks which, if not done correctly, would reflect badly on the legal team. However, a well-established partnership with an ALSP is now viewed as an invaluable asset for both law firms and corporate legal departments. ALSPs bring proven expertise in many areas and their ability to deliver consistent, high-quality results at a fraction of the cost of traditional approaches has eroded much of the doubt that once surrounding them. As the role of ALSPs becomes more prominent, they will no longer be perceived as “alternative” but rather as integrated into the core operational strategies of law firms and legal departments. The question for 2025 isn’t whether ALSPs will play a role in the legal industry but whether their contributions are such that they are no longer viewed as “alternative.” Looking Ahead in 2025: ALSPs Can Help Deliver Greater Impact from AI, Faster This year will be pivotal for legal services providers. Roles and offerings will evolve as AI technologies continue to develop, adoption gathers pace, and AI becomes embedded in legal service delivery. As a pioneering ALSP with over 25 years in the legal industry, Integreon is well positioned to guide clients through their transition into AI enhanced services. Technology agile with deep industry expertise and supported by a team of experts from key industry sectors, Integreon is committed to providing clients with unbiased insights and support as we navigate the months ahead. Having experienced the evolution of eDiscovery technology over the last two decades, we have a practical and pragmatic approach to review projects, strongly believing in the critical role that humans play in the process. Whilst AI may excel at reducing data sets and narrowing the focus for review, skilled professionals remain essential to ensure these processes are conducted in a defensible manner and to provide the necessary validation. We see the year ahead as an opportunity to harness the immense potential of technology whilst providing our clients with the assurance that they are supported by a trusted partner.
Unlocking Creativity
High-growth brands know that fostering creativity is essential to business success. If creativity drives growth, how do you drive creativity?
On-Demand Webinar: Regulatory Edge – Keys to Saving Millions in the Evolving EU Market
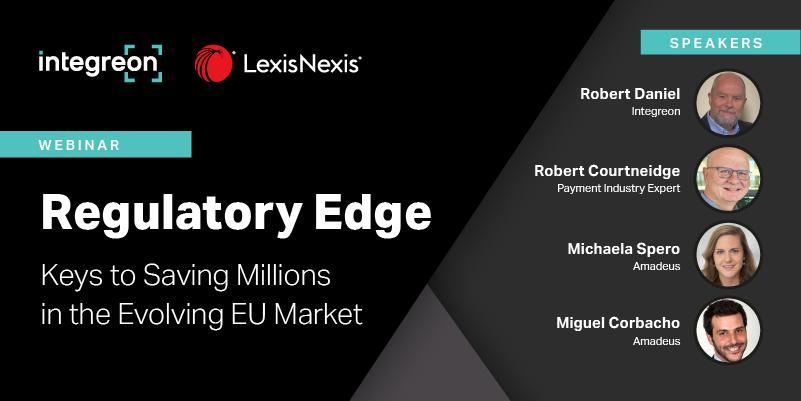
In a regulatory environment that’s changing at an unprecedented pace, fintech and payments companies are under increasing pressure to stay compliant and avoid costly fees. In this webinar, co-hosted by Integreon and LexisNexis, industry experts share insights, trends, and actionable strategies to help your organization navigate the complexities of compliance in today’s fast-changing landscape. What You’ll Learn 1. Regulatory Landscape Overview Gain a comprehensive understanding of recent EU fintech and payments regulations, upcoming regulatory forecasts, and examples of the high costs of non-compliance. 2. Spotlight on Key Regulations Take a deep dive into essential regulations, such as the Payments Services Directive 3 (PSD3) and the DORA, with guidance on actionable steps and best practices to simplify compliance, reduce risks, and achieve efficient implementation. 3. Regulatory Compliance as a Competitive Advantage Learn how proactive compliance monitoring can drive business value. Featuring one of our clients, this session introduces Integreon’s Regulatory Compliance Monitoring Service, using LexisNexis’ solutions, Newsdesk to demonstrate how real-time regulatory alerts can help avoid costly mistakes, streamline operations, and build stronger customer and partner relationships. If you’re focused on staying at the forefront of regulatory changes and minimizing compliance risks, this webinar is for you. Watch now Speakers Robert DanielSenior Director, SME Financial Services / Discovery / Workflow, Integreon With over 25 years of experience, including a distinguished tenure at Bank of America, Robert brings extensive expertise in legal discovery, regulatory investigations, and e-Discovery processes. His proven leadership, strategic insights, and hands-on expertise make Robert a trusted partner in addressing complex discovery and compliance challenges for current and future Integreon clients. Robert CourtneidgePayment Industry Expert and Consultant, Independent Industry Expert As an industry pioneer, Robert helps payments firms transition to the digital age, addressing challenges like blockchain integration, digital currencies, and evolving consumer demands. With traditional financial services at risk of losing relevance to tech disruptors and Gen Z preferences, he guides businesses to pivot successfully, leveraging technologies like DLT, stablecoins, and CBDCs while maintaining synergy with traditional financial frameworks. Michaela SperoSenior Legal Counsel, Competition and Regulatory Affairs, Amadeus Michaela is Senior Legal Counsel, Regulatory Affairs at Amadeus, a global technology company providing solutions for the travel industry. Michaela advises the company on regulatory compliance and strategy across several areas, including coordinating innovations in regulatory tracking through the Regulatory Radar, responding to inquiries from regulators, providing regulatory counseling across business units, and advising on regulatory aspects of mergers and acquisitions. Miguel CorbachoLegal Counsel Financial Regulations, Amadeus Miguel is Legal Counsel, Regulatory Affairs at Amadeus, a global technology company providing solutions for the travel industry. Miguel advises the company on financial regulatory compliance matters to both Amadeus and Outpayce (an e-money institution providing payment services for the travel industry. Prior to joining Amadeus, he was a Senior Associate in the International Capital Markets group in Allen&Overy (now called A&O Shearman) and also worked for KPMG Abogados in the financial regulatory department and in BBVA as in-house Counsel.
Integreon Earns Rigorous Financial Supplier Qualification System (FSQS) Certification Endorsed and Required by Leading Financial Institutions
Successful completion of stage 1 and 2 certification requirements provides Integreon clients with confidence in multiple areas of compliance, including DORA, which goes into effect January 17, 2025 December 12, 2024 – (LONDON) – Integreon, a leading global provider of tech-enabled legal, creative, and business solutions, has successfully completed the Financial Services Qualification System (FSQS) registration certification, a rigorous accreditation process requiring Integreon to be subject to a comprehensive assessment in the areas of business continuity, financial, insurance, health and safety, IT and information security, anti-bribery, recruitment, operational risks, fraud, responsible business governance and records management, environmental, sustainability and privacy. “Integreon’s alignment with these stringent standards reaffirms our dedication to operational excellence and responsiveness to evolving industry challenges, as well as reinforces our position as a trusted partner to our global clients,” said Integreon CEO Subroto Mukerji. FSQS is an accreditation tool used by leading UK and EU financial organizations including Santander, Lloyds Banking Group, Metro Bank, Bank of Ireland, and the Bank of England, to name a few. Partnering with Integreon offers financial services and other businesses within highly regulated sectors benefits such as alignment with regulatory requirements, reduced procurement timescales, high-quality validated information, and cost and resource efficiency. This milestone underscores Integreon’s unwavering commitment to delivering exceptional, secure, and compliant services to the banking, financial services and insurance communities, sectors we have served for over 25 years. Meeting DORA Requirements Ahead of Schedule This certification is particularly timely as the Digital Operational Resilience Act (DORA) is set to take effect in the UK on January 17, 2025. The introduction of DORA requires financial institutions to adhere to strict guidelines for protecting against Information and Communication Technology (ICT)-related incidents, encompassing measures for prevention, detection, containment, recovery, and repair. DORA specifically addresses ICT risks by establishing clear rules for ICT risk management, incident reporting, operational resilience testing, and the oversight of third-party ICT risks. “Achieving FSQS accreditation highlights the exceptional strength, expertise, and dedication of our Infosec and other essential teams across the organization that participated in the certification process. This is a true testament to Integreon’s ability to provide clients with the most secure and compliant services,” said John Wei, CTO at Integreon. About Integreon Integreon is the trusted, global provider of legal, creative and business outsourced solutions to corporations and law firms seeking to expand their capabilities and transform their performance. The company’s 3,500+ professionals provide expert support across a range of managed services—from creative design, content delivery and administrative support to legal and compliance. With global delivery centers on three continents, Integreon delivers round-the-clock service in 50+ languages and is deeply committed to client success, consistently delivering innovative, tech-enabled solutions that improve agility and efficiency to drive business performance. Integreon is owned by EagleTree Capital, a leading New York-based middle-market private equity firm with over $5 billion of assets under management. For more information about Integreon’s range of services, email [email protected], visit www.integreon.com and follow Integreon at LinkedIn, Twitter, and Facebook.
Post-Breach Data Review: 5 Reasons Why You Should Not Go at It Alone
After a data breach, organizations need to understand the scope of the incident in order to quickly resolve it and ensure they are able to meet notification requirements. The urgency often leads to the misguided belief that conducting the investigation internally, with current team members who seemingly know the data best, is the most efficient approach. While the intent might be good, in-house investigations can result in downstream regulatory and legal consequences. Post-breach data mining is a specialized field that requires expertise to handle breach investigations correctly and efficiently. Take Uber’s notorious handling of its 2016 breach where threat actors were paid $100,000 in bitcoin to sign non-disclosure agreements (NDAs) regarding the hack. Uber opted for self-investigation and ultimately faced severe consequences due to inadequate and much delayed reporting. Uber’s Chief Security Officer (CSO) was also convicted by the Federal Trade Commission (FTC) of attempting to cover up the breach. Not all post-breach self-investigations are as nefarious as Uber’s. However, the fallout from conducting a well-intentioned yet insufficient internal investigation can still be drastic. Equifax learned this lesson the hard way after it experienced a cyberattack followed by a self-conducted post-breach investigation that did not end well. Following Equifax’s 2017 breach, they faced significant backlash after it was revealed that more comprehensive third-party involvement could have avoided delays and mishandling of the investigation. Equifax received heavy penalties and a lasting reputational hit, which underlines the potential pitfalls of inadequate self-investigations. Data protection regulations impose significant penalties for inadequate data breach reporting. To avoid these penalties, working with experienced third-party data mining experts ensures both compliance and credibility. Since The General Data Protection Regulation (GDPR) in the EU and the Health Insurance Portability and Accountability Act (HIPAA) in the U.S. are frameworks that emphasize transparency and objective post-incident reporting, the role of third-party expertise becomes critical in incident response and regulatory adherence. Here are five reasons why you should choose a specialized, third-party data mining provider, instead of handling the data review internally. 1. Specialized Tools and Expertise for Data Processing Third-party vendors have the technology, tools, and expertise to narrow the scope of the review efficiently and defensibly. Specialized data mining vendors can use forensics tools to target only documents accessed or exfiltrated by the threat actor rather than the entire data set the threat actor could have accessed. Professional eDiscovery tools allow for advanced deduplication to ensure that each document is only being reviewed once and enable enhanced searching functionality to perform effective programmatic data mining to isolate the documents most likely to contain reportable data. 2. Defensible Data Culling Data mining vendors are experts with all things data, and work hand in glove with breach counsel to assess the applicable jurisdictions and regulations for each project. Using this information, data mining vendors cultivate bespoke search term lists for each matter and tailor advanced culling methodologies specific to the organization’s industry. Data mining vendors also understand which search terms yield higher relevancy rates and those that result in more false hits. Also, data mining vendors work with the organization to further reduce the data population using the proprietary in-house knowledge of the data to remove pockets of non-relevant documents. Thus, data mining vendors, leveraging an organization’s knowledge of the data, can defensibly cull the data set down, making the undertaking more cost effective. 3. Trained Review Teams to Scale with Quality Control Processes Third-party vendors conduct data mining reviews every day and can train reviewers who are then ready to hit the ground running. The reviewers know what to look for and how to make their way most efficiently through the documents. Pods managed by senior reviewers ensure that each reviewer is receiving prompt feedback and that the team is aligned and following a consistent approach. Data mining vendors also utilize robust quality check processes to ensure that data is collected accurately and examine anomalies requiring further review. Importantly, third-party vendors can scale up quickly to meet tight regulatory deadlines on projects of any size. 4. Technologists with an Extensive Toolkit to Conquer Difficult Documents and Entity List Consolidation Third-party data mining providers bring technical expertise and efficient processes to post-breach investigations, especially in areas like data extraction from complicated, lengthy files, unstructured sources, and deduplicating and consolidating the final entity list. This expertise is often lacking in-house and is costly to develop internally. Without specialized techniques to extract sensitive information from lengthy, complicated files, the review process can be extremely time-consuming, tedious, and expensive to undertake. Once the review is finished, it is necessary to conduct a technical process to consolidate and merge entities within the final notification list. This is essential to ensure a proper risk assessment for individuals, to determine whether jurisdictional notification thresholds have been reached, and to make certain that everyone is only notified once. 5. Reputation, Regulatory Compliance, and Legal Risk Management A third-party investigation helps reassure clients, stakeholders, and the public that the breach is being handled with due diligence. An independent investigation signals transparency and accountability, which can be crucial for brand reputation in the wake of a cyber incident. Third-party data mining vendors can help companies comply with data privacy laws, such as GDPR, HIPAA, or the Family Educational Rights and Privacy Act (FERPA), and manage the risk of non-compliance. Vendors often have dedicated teams familiar with global regulations and which sensitive data elements to extract for specific groups, which is essential for multi-national firms. Third-party investigations can limit liability by ensuring proper documentation, consistent processes, and credible findings. This is crucial in the event of litigation or regulatory scrutiny following a breach. In conclusion, the importance of thorough and unbiased post-breach investigations cannot be overstated. By choosing a third-party data mining provider, organizations can ensure compliance, credibility, and a faster more effective data breach response. Don’t let the aftermath of a breach become a bigger problem than the breach itself. Make it part of your incident response plan to partner with a provider you can rely on if
How AI is Reshaping Cyber Insurance
This article first appeared on www.insurancethoughtleadership.com. View the original article here. AI emerges as both threat and solution in cyber insurance, reshaping risk assessment and breach response. AI is transforming the work of professionals everywhere. Unfortunately, that includes cybercriminals. These threat actors can now harvest and analyze more data than ever, automate phishing attacks and mimic human voices with alarming accuracy, allowing them to penetrate the defenses of the most sophisticated organizations. According to Microsoft’s latest digital defense report, cybercriminals and nation-states launch more than 600 million attacks against the company’s customers daily. That’s nearly 7,000 per second. The advent of generative AI will likely increase the severity and frequency of those cyberattacks, which could drive claims and premiums. However, AI also offers immense potential to benefit the cyber insurance market. It can counter costs associated with cyberattacks, both in the reactive phase of breaches and in proactive risk mitigation. More cost certainty with AI-powered data mining One of the most significant costs in assessing the potential damage and cause of cyberattacks is data mining — the process of analyzing logs, files and other digital information in search of clues about a breach. This work helps organizations and the industry better understand and manage cyber risks. Before the widespread commercialization of generative AI, human analysts and lawyers predominantly conducted this work, sifting through millions of documents to determine if sensitive information was exposed or exfiltrated and what required reporting to authorities. Today, generative AI and machine-learning tools offer ways to automate more of the data-mining process, delivering faster, more accurate results — and, crucially, with more cost certainty. Consider a breach involving sensitive data points like tax identification numbers or Social Security numbers. Confirming whether those numbers were exposed at a global company would require months of work by human analysts. With the right search instructions and parameters, AI-powered tools can search for the numbers instantly. Human oversight still needed The results cannot be blindly trusted. As effective as the technology is, it’s not a standalone solution. Human input and oversight remain crucial. Getting accurate results and avoiding false positives require cyber experts with extensive experience searching for sensitive data points and understanding the context in which they appear in documents. That experience allows them to provide the right prompts and test the results to ensure accuracy. Without human expertise, data will continue to be vulnerable to attack. Additionally, the cost savings of an AI-powered data-mining operation could be lost if lawyers challenge the findings and must conduct their own investigation. The technology may stand alone one day, but it’s not there yet. Generative AI’s next frontier: pre-breach maintenance A data breach often surprises company executives. Many are unaware of the sensitive information exposed. Sometimes, they didn’t appreciate the number of people not following company guidelines around data preservation. Other times, they were unaware employees were using private messaging apps to transmit files to personal devices. Occasionally, executives weren’t informed that data relating to spun-off or sold entities remained undeleted. These realizations are spurring organizations and the cyber insurance industry to rethink ways to improve pre-breach data maintenance. Cyber health scans Despite the billions of dollars that organizations spend yearly on building cyberinfrastructure, attacks persist. That’s why there is unprecedented focus on the content of the data — rather than the walls around it. This new approach could significantly alter how cyber insurance companies assess risk. AI development is helping to power the new approach. With large language model-based tools, organizations can receive a data scan that generates a heat map detailing sensitive data and potential risk levels in the event of a cyberattack. This allows companies to understand their vulnerable data before an attack. A scan can give organizations an outline of the internal data stored in their systems. With that picture, they can improve data governance by making informed risk-mitigating decisions, such as removing or further securing sensitive digital information. By making that information more secure, organizations make ransomware attacks less inviting and reduce their costs and risks. AI’s positive influence is just beginning AI’s application to the cyber insurance market has only begun to show its impact. However, by leveraging AI for both pre- and post-breach processes, organizations and insurers can reduce breach-related costs while improving risk management.
Navigating PERM Recruitment Successfully
https://www.youtube.com/watch?v=EoqizFxgKYI For global mobility professionals, dealing with the PERM recruitment process can be a major challenge. Gain insights from one of our immigration services specialists, Kim Calabro, as she shares PERM trends and best practices. Want to learn more about Integreon’s Immigration Solution? Send us a brief message so we can provide a tailored services plan that meets your needs and timeframe.
On-Demand Webinar: Bring Predictability to the Unpredictable: Reduce Spiraling Costs for Incident Response
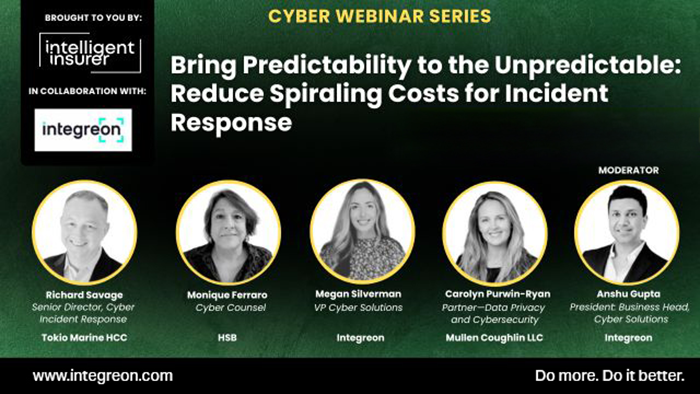
Cyber breach costs are skyrocketing, and staying on top of incident response is crucial for both insureds and insurers. Learn how to manage unpredictable costs and work more efficiently with vendors in our on-demand webinar brought to you by Intelligent Insurer. Learn more how Integreon can help you reduce the cost of cyber incident response Learn more Watch now