What is your why?
Defining and understanding the “why” of your business – to sharpen strategy, strengthen brand purpose, build trust and energize your team.
Best Practices for Controlling Cyber Incident Response Costs
This is Part 2 of a 2-part series titled The Complete Guide to Reducing Cyber Incident Response Costs in the Legal Industry. Download the guide here. According to a recent IBM study, the cost of a data breach is the highest it has ever been, with 75% of the increase being due to the cost of lost business and post-breach response activities. The lesson? Investing in post-breach response preparedness can help dramatically lower breach costs. Below we break down five things law firms should do now to best recover from a cyber incident. 1. Have a cyber incident response plan A cyber incident response plan (CIRP) can help prepare, guide, and protect a firm during and after a cyber incident. Based on a report by Ponemon Institute, companies without a formal CIRP pay 58% more per breach compared to those with structured, tested response protocols. Yet, according to the ABA, only 34% of law firms have an incident response plan in place. All CIRP plans should include the following efforts: Define the purpose of the plan and the types of cyber incidents it covers (data breaches, ransomware, phishing attacks, etc.). Define the roles and responsibilities of the team, including internal members (IT, PR, HR, etc.) and external partners like cybersecurity consultants. Establish criteria for categorizing incidents by severity and impact. Develop a framework for how to identify and report potential incidents (monitoring tools, employee reporting procedures, etc.). Outline step-by-step procedures to contain, eradicate, and recover from an incident, including specific protocols for diverse types of incidents. Define internal and external communication strategies during an incident, including templates for notifying stakeholders, clients, and regulatory bodies. Address regulatory requirements (GDPR, CCPA, etc.) for reporting incidents and preserving evidence. Outline steps to restore systems and data to normal operations, including a post-incident review process to identify lessons learned and improve the plan. Detail regular training programs for employees and the incident response team. Include simulated tabletop exercises to test the plan. List the tools, technologies, and resources in use across the firm (firewalls, SIEM systems, etc.). Define a schedule for reviewing and updating the plan to ensure it remains current with evolving threats and organizational changes. 2. Outline clear data management processes Effective data management begins with establishing clear and streamlined processes. Start by decluttering your data collection methods. This ensures you are only gathering what is necessary. Excessive or irrelevant data can slow down operations and inflate storage costs unnecessarily. By focusing on quality over quantity, you can classify and track data more efficiently, maintaining an organized system that allows for faster access and better decision-making. 3. Encourage cross-team collaboration Cross-team collaboration is another critical component of robust data management. Encouraging your firm’s IT and InfoSec teams to work closely ensures data security and infrastructure remain top priorities throughout the management process. Legal and communications teams should also be engaged regularly to align with compliance standards and maintain transparency. By breaking down silos and fostering collaboration, businesses can create a unified approach to data management that minimizes risks. Read Here 4. Purchase a comprehensive cyber insurance policy Understanding Cyber Insurance Coverage is another essential part of a viable Cyber Incident Response Plan. When doing your pre-purchase research, look for coverage for breach response, data restoration, privacy breach notification costs, and data privacy litigation coverage. Some cyber policies offer “Outside the Aggregate Limit” breach response coverage, which preserves the policy aggregate limit for class action litigation and other high-exposure risk profiles. 5. Follow correct data mining protocols Today there is an increased threat of data breach class actions. In fact, according to the Duane Morris Class Action Review – 2025, plaintiffs filed more data breach class actions in 2024 than in any other year, doubling the number filed in 2022. Effective data mining plays a significant role in managing regulatory and litigation risk. The goal is to identify exactly what data was accessed or exfiltrated, no more and no less. To support that, it is essential to: Limit the data population by engaging a forensic partner to isolate the impacted data set. This helps reduce scope, cost, and downstream exposure. Work closely with breach counsel to ensure compliance with regulatory requirements, such as GDPR and state-level breach notification laws, and to ensure the overall response is legally sound. Leverage targeted data mining workflows to quickly identify affected individuals and data types and document the methodology to support later scrutiny. Maintain transparency and ethical rigor throughout the process, especially when interpreting results that could have real-world consequences for affected individuals. While data mining costs can vary depending on data quality, volume, and complexity, there are proven ways to bring greater cost control and predictability: Use advanced culling and pre-processing to reduce the review set before manual analysis begins. Secure fixed per-document pricing for the manual review phase to avoid budget overruns. Partner with a vendor known for delivering high-quality, defensible work. A well-executed initial pass can eliminate costly rework and reduce the risk of notification errors that may trigger additional liability. In today’s litigation-heavy climate, an unfocused or poorly executed data mining effort is a liability. Performing it diligently by following the steps outlined above is one of the most effective ways to limit future risk exposure. Law firms must invest in both protecting themselves against cyber crime and preparing for an inevitable attack. These recommendations serve as a starting point for developing a solid strategy, but it is most important to see these as moving targets. As technology innovation accelerates, law firms will need to continuously adapt. For guidance on how to best futureproof your law firm against cyber threats, reach out to the Integreon team at [email protected]. If you are interested in accessing our full guide, The Complete Guide to Reducing Cyber Incident Response Costs in the Legal Industry, download it here. Read the full guide here What’s included: Best practices: Cyber Incident Preventions Controlling Cyber
Unleashing Creativity in Financial Services Marketing While Staying Compliant
In the heavily regulated world of financial services, marketers often find themselves walking a tightrope: how do you create bold, differentiated campaigns while staying firmly within compliance lines? At a recent FCS webinar titled “Coloring Inside the Lines: Marketing Boldly While Remaining Compliant,” leaders from Bank of America, Invesco, Jennison Associates, and Integreon shared how marketing and compliance can be collaborative allies—not adversaries. Here’s what we learned: 1. Bring Compliance in Early—and Often Tip: Involve compliance as soon as campaign ideation begins—not after design is finalized. Mari Lee, SVP, Marketing of Bank of America said it best: “My secret sauce is to involve compliance early, often, and all throughout.” Getting input from compliance during the planning phase helps surface potential roadblocks early and creates time for creative workarounds, reducing last-minute rewrites and delays. 2. Build a Collaborative Relationship Tip: View compliance as a strategic partner, not a gatekeeper. Compliance shouldn’t be the “department of no,” said Keye Chang, Sr. Compliance Officer, Invesco. Instead, he encourages marketing teams to think of compliance as their co-pilot, helping them get creative ideas over the line. “The best outcomes happen when we understand the destination and work together on how to get there—without regulatory trouble.” 3. Communicate Constantly and Transparently Tip: Set up regular check-ins, share editorial calendars, and create shared visibility into review queues. Katherine Boylan, SVP, Director of Integrated Marketing, Jennison Associates emphasized the value of transparency and routine. Her team uses shared tools like the compliance software, Red Oak, to track content reviews and timelines. They also maintain live editorial calendars and documentation around compliance guidelines to keep everyone aligned. Chang and his colleagues publish and share a regular newsletter on financial services regulations that Invesco marketers should keep in mind when creating campaigns. 4. Use Technology to Streamline Workflows Tip: Invest in approval and workflow tools that bring visibility and efficiency to marketing-compliance processes. Whether it’s Red Oak, a MAP (Marketing Approval Portal), or another system, having a platform that connects marketing, legal, and compliance teams can dramatically improve speed and accuracy. Boylan also uses templated content for quarterly materials, reducing repetitive work and freeing up time for innovation. 5. Be Bold—With Guardrails Tip: Bold marketing is possible when paired with thoughtful compliance collaboration. Lee recommends looking outside the financial services category for inspiration for new marketing ideas. She also gave an example of how she pushed the envelope this year by creating dynamic data chart visualizations for one of her bank’s thought leadership content offerings. Her approach to getting compliance on board with something new? Start conversations even earlier than you think you should, show strawman mockups early, include legal, compliance, and registered principal experts and collaborate with them often and all throughout your planning process. 6. Embrace “Creative Compliance” Tip: Encourage compliance teams to offer alternatives instead of blanket rejections. Chang likened compliance to helping marketing color inside the lines—with the right tools. Instead of saying “no,” his team often suggests, “Try this instead.” In some cases, they’re even applying creativity to compliance communications by producing TikTok-style training videos to demystify regulatory concepts for internal teams in fun, digestible ways. 7. Look Ahead: AI and Regulatory Trends Tip: Prepare now for evolving regulations—especially around performance marketing and artificial intelligence. Panelists agreed: AI is both an opportunity and a risk. From speeding up internal workflows to creating images and content, tools like Norm AI are under exploration. But all agreed: AI must be used responsibly, with governance frameworks, transparency, and human oversight at every step. Final Thought: Creativity and Compliance Aren’t Mutually Exclusive The most successful marketing teams don’t fight compliance—they invite them in as early allies. As Chang reminded us (with a nod to Finding Nemo), “Compliance is not food. We’re friends.” By fostering mutual respect, aligning goals, and planning ahead, marketing professionals can boldly break through the noise—while still coloring inside the lines.
CSR Report 2025
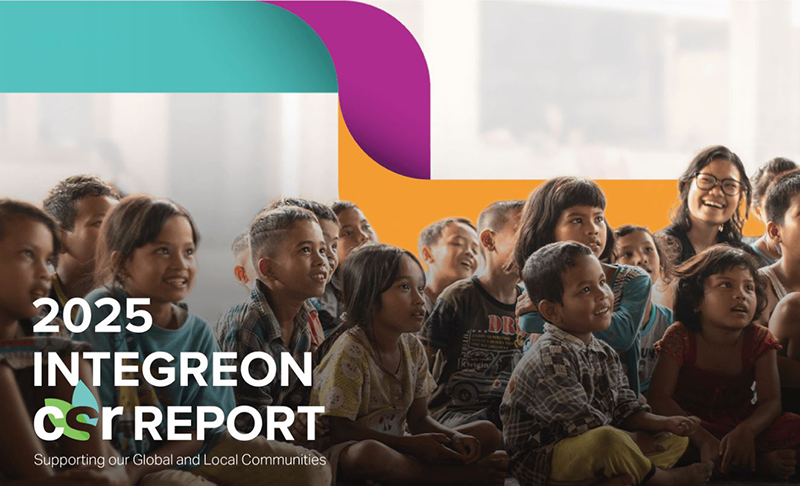
Our 2025 CSR Report highlights our unwavering commitment to the communities and charities that improve the lives of many people worldwide. For over 25 years, Integreon has prided itself on initiatives focusing on three key pillars: Education, Healthcare, and the Environment. To learn more about our global CSR efforts, read the full report below: Read the full report
Best Practices for Cyber Incident Prevention for Law Firms
This is Part 1 of a 2-part series titled The Complete Guide to Reducing Cyber Incident Response Costs in the Legal Industry. Download the guide here. In our global, digital-first economy, cyberattacks are no longer isolated incidents targeting large organizations. They are a very real threat to businesses of all types and sizes, and law firms are a common target of cyber criminals. It is not difficult to see why law firms are often targets of cyber crime. The information collected by firms – from trade secrets, intellectual property, merger, and acquisition details to personally identifiable information and attorney-client privileged data – is particularly attractive to cyber criminals. The American Bar Association (ABA) reports that 42% of law firms with 100 or more employees have experienced a data breach. What often gets underestimated is the cost of recovering from a cyber attack. A recent IBM report found the global average cost of a data breach in 2024 was $4.8 million – a 10% increase over last year and the highest total ever. How can law firms better safeguard their data and fortify their systems to help prevent cyber attacks from occurring? There are three primary areas law firms can focus on to safeguard against cyber threats. 1. Firmwide Best Practices Creating clear policies for employees and contractors to follow when using communications is one step to take. Many law firms are doing this. As of 2024, law firms with policies in place to govern employee behavior was as follows: 55% – Email use 51% – Internet use 50% – Computer acceptable use 50% – Remote access 44% – Social media Source: ABA There are several technical ways to strengthen your firm’s defense against threats. Control network access by establishing clear permissions and limiting entry points to critical systems. The security boundary should be as small and as controlled as practical to minimize the attack surface available to hackers. Set up firewalls to act as a first line of defense that can block unauthorized access and help monitor incoming and outgoing traffic. Use multifactor authentication (MFA) to add an extra layer of protection. This requires users to validate their identity through a second source, such as a code or biometric scan. (While a free service, the ABA reports only 54% of firms have MFA in use.) Apply network segmentation to enhance security by dividing the network into smaller sections, helping to contain potential breaches and minimize damage. Put active threat intelligence and regular vulnerability testing into place. 2. Employee Best Practices According to Verizon’s 2025 Data Breach Investigations Report, 68% of all breaches involve human error, from phishing clicks to misconfigured security settings. Employees must be educated in how to maintain good digital hygiene. Integreon’s Chief Technology Officer, John Wei, agrees. “Defending against cyber threats requires a highly collaborative approach, involving not just a select few cybersecurity professionals, but everyone across the organization,” says Wie. Here are just a few important habits that should be included in your new hire onboarding and ongoing employee education efforts. Avoid reusing passwords across multiple accounts to minimize the risk of unauthorized access. Limit device access to only trusted individuals. Sharing devices with others can expose sensitive information. Use only secure Wi-Fi networks to help prevent potential security breaches and unauthorized access to personal and other data. Report any suspicious email activity, as phishing emails can be extremely sophisticated. According to an FBI report, cybercriminals stole approximately $2.9 billion through business email compromise (BEC) frauds, with law firms among the most common targets. Read Here 3. Detection and Response Automation Best Practices Detection and response automation is revolutionizing how firms address cybersecurity threats. In fact, according to IBM, AI-driven security automation saves companies $2.2 million per breach by cutting response times and improving containment. Security Information and Event Management (SIEM) platforms can monitor and analyze log data from various systems. These systems detect suspicious activity in real time and allow teams to quickly mitigate risks. Automated incident response tools take this a step further by eliminating the delays that come with manual intervention. If a threat is detected, these tools can immediately isolate compromised systems, block malicious traffic, or trigger other predefined actions to contain and neutralize the risk. Machine learning-based security solutions further enhance detection capabilities, leveraging AI to identify advanced threats and anomalies. These systems learn over time, adapting to the normal behavior of a network and flagging deviations that could indicate a breach. In the second blog of this two-part series, we will discuss how to control cyber incident costs once a cyber attacks has occurred. Read the full guide here What’s included: Best practices: Cyber Incident Preventions Controlling Cyber Incident Response Costs Download the guide
Consero Legal Operations Forum
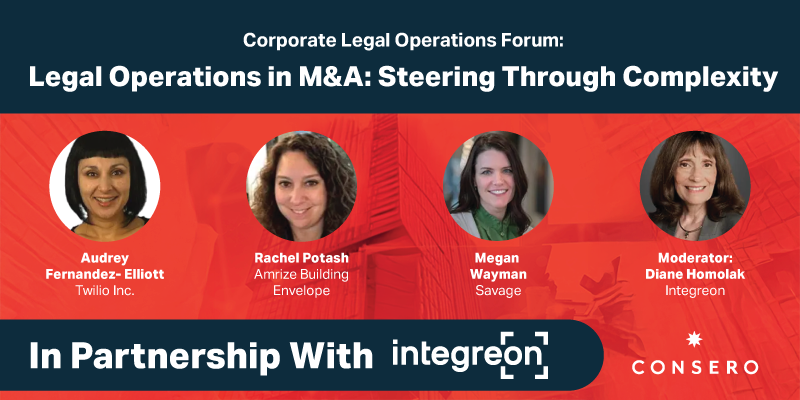
Leesburg, Virginia – July 14-16, 2025 This two-day event includes active panel discussions and breakout sessions, and is designed for legal operations professionals interested in leveraging new practices and tools to stay competitive and lead transformative change. Integreon’s Diane Homolak will facilitate a panel discussion with Audrey F.-Elliott, Twilio; Rachel P., Amrize and Megan Wayman, Savage on “Legal Operations in M&A: Steering Through Complexity.” Event Details
The L Suite Legal Ops x GC Offsite
Sonoma California – July 15-17, 2025 Legal leaders today must be more than legal experts, they must be systems thinkers, culture builders, and strategic operators. This exclusive Offsite will celebrate the legal professionals who are not just adapting to business demands, but shaping them. You’ll explore how legal ops and GC-operators are accelerating innovation, embedding agility, and becoming essential change agents across their organizations. Whether you’re launching a new initiative, driving AI adoption, or optimizing for speed and scale, this Offsite will equip you with strategies to amplify your influence and drive action. You’ll hear from bold thinkers and operators making high-impact decisions every day. Join us for 3 days in sunny Sonoma and help ignite what’s next for legal leadership and operations. Join the Waitlist
On-Demand Webinar: Legal Ops: Top Challenges and KPIs
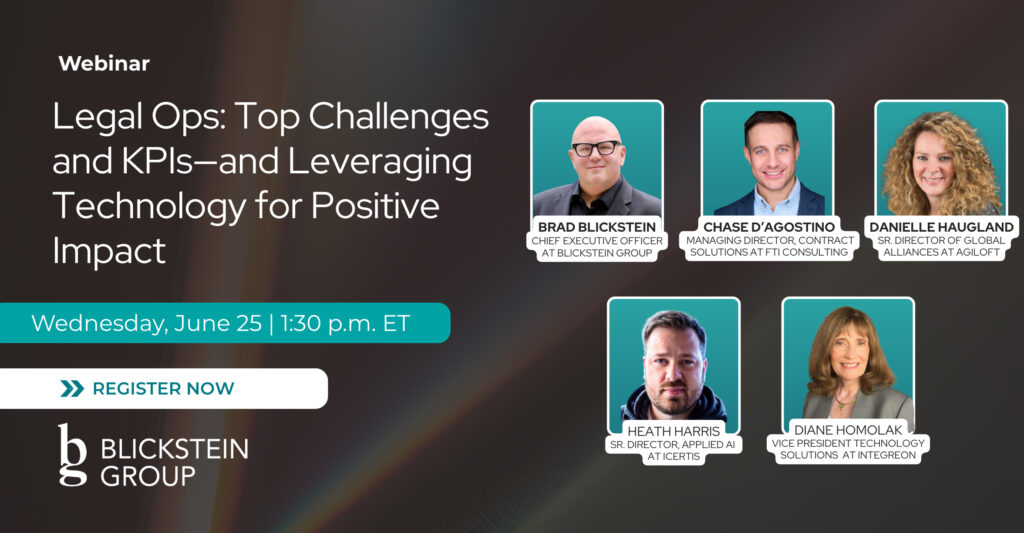
In this hour-long webinar produced by the Blickstein Group, contracts solutions experts, including Diane Homolak, VP, Technology Solutions at Integreon, discuss how legal ops can best take advantage of disruptive technologies to improve operations and save time and cost. Learn more about Integreon’s Contracts Solutions here. Watch now